About RajSecure
RajSecure is an international cybersecurity consultancy and security technology lab dedicated to offensive vulnerability testing, API and application security, cloud hardening, and defensive software innovation.
Operated by RAJSECURENEXA CYVEXA PRIVATE LIMITED • Incorporated in India • Serving international clients globally.
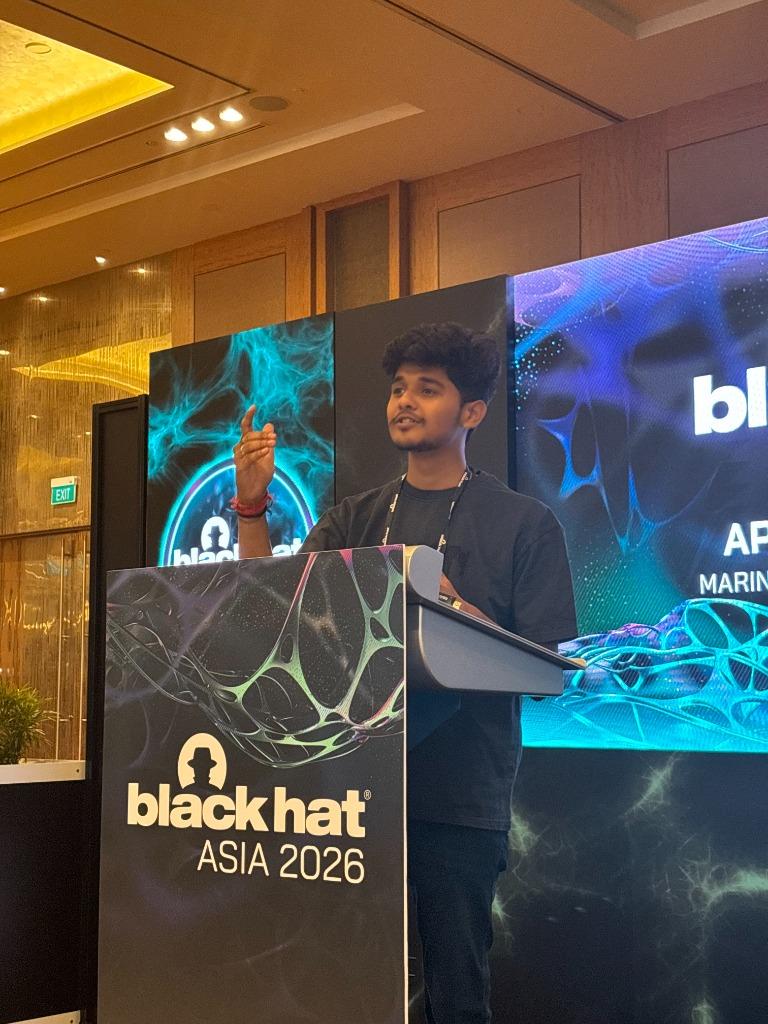
FOUNDER & CHIEF EXECUTIVE
Raj Kumar
Founder & CEO, RajSecure
Raj Kumar is a cybersecurity entrepreneur and offensive security researcher who founded RajSecure to address the critical gap between high-volume automated vulnerability scanners and real-world adversarial exploitability.
He directs the firm’s offensive assessment methodologies, penetration testing frameworks, and proprietary software initiatives. His philosophy combines attacker-informed threat modeling with engineer-grade remediation: every vulnerability deliverable must include verifiable proof-of-concept evidence and concrete code-level patch guidance that developers can implement immediately.
In addition to consulting, Raj leads the development of RajSecure’s software ecosystem, including RajSecure Shield (a personal digital safety firewall against coercion and digital leverage), RajSecure AI (an adversarial LLM testing suite), and RajSecure EPR (a cryptographic evidence protection and incident response framework).
Global Community & Industry Exposure
Black Hat Conferences & International Research
Raj actively engages with premier international cybersecurity research communities, including the Black Hat conference network, to monitor bleeding-edge zero-day mechanics, cloud IAM escalation paths, and offensive AI manipulation techniques.
GLOBAL REACH
Engineered for International Clients
RajSecure operates from India with an international-first delivery architecture. We serve technology organizations, SaaS scale-ups, and enterprises across the world’s most demanding security environments.
United States
USPractice Focus: SaaS, Cloud & SOC 2 Readiness
United Kingdom
GBPractice Focus: FinTech, Open Banking & AppSec
Germany
DEPractice Focus: Enterprise Security & BSI IT-Grundschutz
European Union
EUPractice Focus: GDPR, NIS2 & DORA Cyber Resilience
Singapore
SGPractice Focus: APAC Financial Hubs & Cloud Infrastructure
UAE & Middle East
AEPractice Focus: Enterprise Scale & Sovereign Tech
OPERATING PRINCIPLES
The RajSecure Standards
We believe in honest, evidence-backed security assessments that prioritize real-world exploitability over scanner noise.
Offensive Security Mindset
We approach your systems from an attacker perspective, finding deep business logic flaws and multi-step attack chains that automated scanners miss.
Evidence-Driven & Zero Noise
Every finding is backed by reproducible Proof of Concept (PoC) evidence and technical observation. No copy-pasted scanner dumps or false positives.
Business-Risk Prioritization
Vulnerabilities are evaluated by their tangible impact on data security, regulatory compliance, and business continuity — not generic scores.
Engineer-Ready Remediation
We deliver clear code-level remediation guidance, architectural recommendations, and direct developer debrief calls to accelerate fixes.
Strict Authorization & NDAs
All testing is strictly authorized under comprehensive non-disclosure agreements, defined boundaries, and secure encrypted data handling.
Verified Retesting Included
We don't just point out flaws; we verify your fixes through structured remediation retesting and provide executive Letters of Attestation.